Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

Google Updated Associate-Cloud-Engineer Exam Questions and Answers by aris

Page: 18 / 26

Google Associate-Cloud-Engineer Exam Overview :

Exam Name: Google Cloud Certified - Associate Cloud Engineer
Exam Code: Associate-Cloud-Engineer Dumps
Vendor: Google Certification: Google Cloud Certified
Questions: 363 Q&A's Shared By: aris
Question 72

Your company requires that Google Cloud products are created with a specific configuration to comply with your company ' s security policies You need to implement a mechanism that will allow software engineers at your company to deploy and update Google Cloud products in a preconfigured and approved manner. What should you do?

Options:

A.

Create Java packages that utilize the Google Cloud Client Libraries for Java to configure Google Cloud products. Store and share the packages in a source code repository.

B.

Create bash scripts that utilize the Google Cloud CLI to configure Google Cloud products. Store and share the bash scripts in a source code repository.

C.

Create Terraform modules that utilize the Google Cloud Terraform Provider to configure Google Cloud products. Store and share the modules in a source code repository.

D.

Use the Google Cloud APIs by using curl to configure Google Cloud products. Store and share the curl commands in a source code repository.

Discussion
Question 73

You’ve deployed a microservice called myapp1 to a Google Kubernetes Engine cluster using the YAML file specified below:
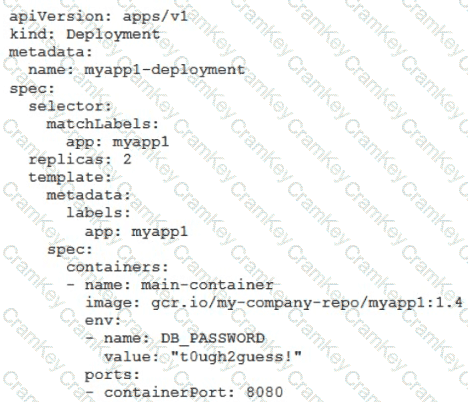
Questions 73

You need to refactor this configuration so that the database password is not stored in plain text. You want to follow Google-recommended practices. What should you do?

Options:

A.

Store the database password inside the Docker image of the container, not in the YAML file.

B.

Store the database password inside a Secret object. Modify the YAML file to populate the DB_PASSWORD environment variable from the Secret.

C.

Store the database password inside a ConfigMap object. Modify the YAML file to populate the DB_PASSWORD environment variable from the ConfigMap.

D.

Store the database password in a file inside a Kubernetes persistent volume, and use a persistent volume claim to mount the volume to the container.

Discussion
Esmae
I highly recommend Cramkey Dumps to anyone preparing for the certification exam.
Mollie Sep 15, 2026
Absolutely. They really make it easier to study and retain all the important information. I'm so glad I found Cramkey Dumps.
Cody
I used Cramkey Dumps to prepare and a lot of the questions on the exam were exactly what I found in their study materials.
Eric Sep 2, 2026
Really? That's great to hear! I used Cramkey Dumps too and I had the same experience. The questions were almost identical.
Osian
Dumps are fantastic! I recently passed my certification exam using these dumps and I must say, they are 100% valid.
Azaan Sep 10, 2026
They are incredibly accurate and valid. I felt confident going into my exam because the dumps covered all the important topics and the questions were very similar to what I saw on the actual exam. The team of experts behind Cramkey Dumps make sure the information is relevant and up-to-date.
Andrew
Are these dumps helpful?
Jeremiah Sep 19, 2026
Yes, Don’t worry!!! I'm confident you'll find them to be just as helpful as I did. Good luck with your exam!
Aliza
I used these dumps for my recent certification exam and I can say with certainty that they're absolutely valid dumps. The questions were very similar to what came up in the actual exam.
Jakub Sep 12, 2026
That's great to hear. I am going to try them soon.
Question 74

A colleague handed over a Google Cloud Platform project for you to maintain. As part of a security checkup, you want to review who has been granted the Project Owner role. What should you do?

Options:

A.

In the console, validate which SSH keys have been stored as project-wide keys.

B.

Navigate to Identity-Aware Proxy and check the permissions for these resources.

C.

Enable Audit Logs on the IAM & admin page for all resources, and validate the results.

D.

Use the command gcloud projects get–iam–policy to view the current role assignments.

Discussion
Question 75

You want to run a single caching HTTP reverse proxy on GCP for a latency-sensitive website. This specific reverse proxy consumes almost no CPU. You want to have a 30-GB in-memory cache, and need an additional 2 GB of memory for the rest of the processes. You want to minimize cost. How should you run this reverse proxy?

Options:

A.

Create a Cloud Memorystore for Redis instance with 32-GB capacity.

B.

Run it on Compute Engine, and choose a custom instance type with 6 vCPUs and 32 GB of memory.

C.

Package it in a container image, and run it on Kubernetes Engine, using n1-standard-32 instances as nodes.

D.

Run it on Compute Engine, choose the instance type n1-standard-1, and add an SSD persistent disk of 32 GB.

Discussion
Page: 18 / 26
Title
Questions
Posted

Associate-Cloud-Engineer
PDF

$31.5  $104.99

Associate-Cloud-Engineer Testing Engine

$37.5  $124.99

Associate-Cloud-Engineer PDF + Testing Engine

$49.5  $164.99
