Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

CompTIA Updated PT0-002 Exam Questions and Answers by boden

Page: 17 / 34

CompTIA PT0-002 Exam Overview :

Exam Name: CompTIA PenTest+ Certification Exam
Exam Code: PT0-002 Dumps
Vendor: CompTIA Certification: PenTest+
Questions: 464 Q&A's Shared By: boden
Question 68

A penetration tester is preparing to perform activities for a client that requires minimal disruption to company operations. Which of the following are considered passive reconnaissance tools? (Choose two.)

Options:

A.

Wireshark

B.

Nessus

C.

Retina

D.

Burp Suite

E.

Shodan

F.

Nikto

Discussion
Andrew
Are these dumps helpful?
Jeremiah Oct 12, 2026
Yes, Don’t worry!!! I'm confident you'll find them to be just as helpful as I did. Good luck with your exam!
Peyton
Hey guys. Guess what? I passed my exam. Thanks a lot Cramkey, your provided information was relevant and reliable.
Coby Oct 9, 2026
Thanks for sharing your experience. I think I'll give Cramkey a try for my next exam.
Ava-Rose
Yes! Cramkey Dumps are amazing I passed my exam…Same these questions were in exam asked.
Ismail Oct 15, 2026
Wow, that sounds really helpful. Thanks, I would definitely consider these dumps for my certification exam.
Sarah
Yeah, I was so relieved when I saw that the question appeared in the exam were similar to their exam dumps. It made the exam a lot easier and I felt confident going into it.
Aaliyah Oct 28, 2026
Same here. I've heard mixed reviews about using exam dumps, but for us, it definitely paid off.
Melody
My experience with Cramkey was great! I was surprised to see that many of the questions in my exam appeared in the Cramkey dumps.
Colby Oct 22, 2026
Yes, In fact, I got a score of above 85%. And I attribute a lot of my success to Cramkey's dumps.
Question 69

You are a penetration tester running port scans on a server.

INSTRUCTIONS

Part 1: Given the output, construct the command that was used to generate this output from the available options.

Part 2: Once the command is appropriately constructed, use the given output to identify the potential attack vectors that should be investigated further.

If at any time you would like to bring back the initial state of the simulation, please click the Reset All button.
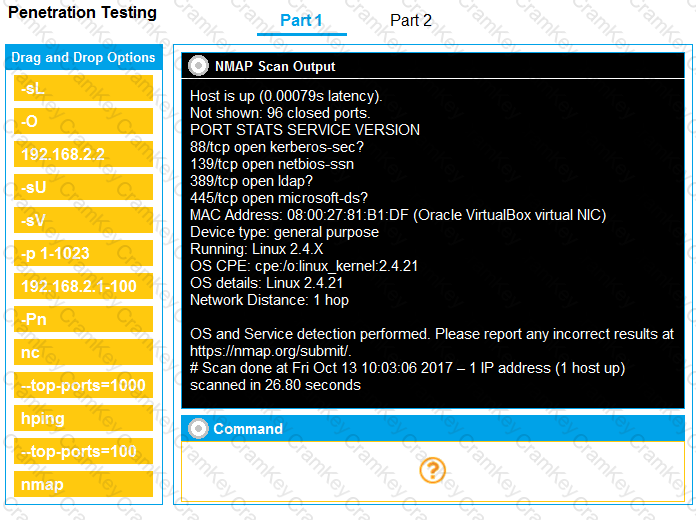
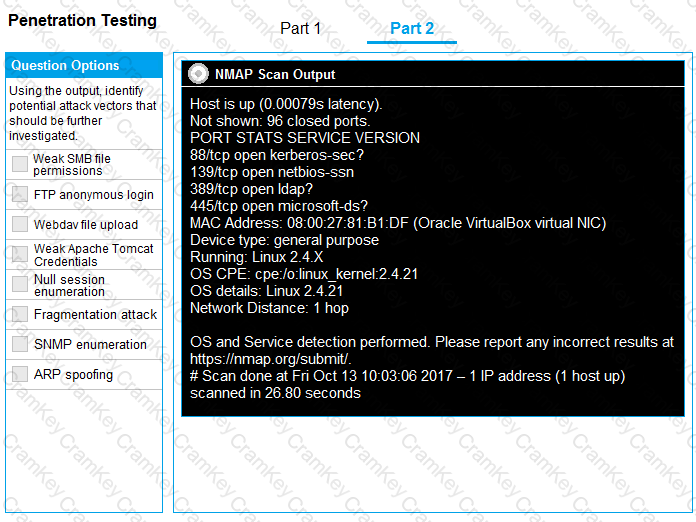
Questions 69

Questions 69

Options:

Discussion
Question 70

A company is concerned that its cloud service provider is not adequately protecting the VMs housing its software development. The VMs are housed in a datacenter with other companies sharing physical resources. Which of the following attack types is MOST concerning to the company?

Options:

A.

Data flooding

B.

Session riding

C.

Cybersquatting

D.

Side channel

Discussion
Question 71

A penetration tester wants to scan a target network without being detected by the client’s IDS. Which of the following scans is MOST likely to avoid detection?

Options:

A.

nmap –p0 –T0 –sS 192.168.1.10

B.

nmap –sA –sV --host-timeout 60 192.168.1.10

C.

nmap –f --badsum 192.168.1.10

D.

nmap –A –n 192.168.1.10

Discussion
Page: 17 / 34
Title
Questions
Posted

PT0-002
PDF

$27.5  $109.99

PT0-002 Testing Engine

$32.5  $129.99

PT0-002 PDF + Testing Engine

$42.5  $169.99
