Halloween Sale Limited Time 70% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: cram70off

CompTIA Updated PT0-002 Exam Questions and Answers by maddox

Page: 19 / 34

CompTIA PT0-002 Exam Overview :

Exam Name: CompTIA PenTest+ Certification Exam
Exam Code: PT0-002 Dumps
Vendor: CompTIA Certification: PenTest+
Questions: 464 Q&A's Shared By: maddox
Question 76

A penetration tester has gained access to part of an internal network and wants to exploit on a different network segment. Using Scapy, the tester runs the following command:
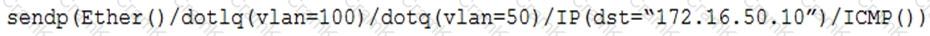
Questions 76

Which of the following represents what the penetration tester is attempting to accomplish?

Options:

A.

DNS cache poisoning

B.

MAC spoofing

C.

ARP poisoning

D.

Double-tagging attack

Discussion
Question 77

A penetration tester ran the following commands on a Windows server:
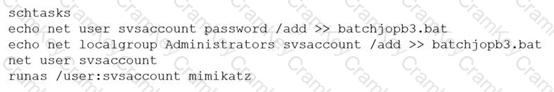
Questions 77

Which of the following should the tester do AFTER delivering the final report?

Options:

A.

Delete the scheduled batch job.

B.

Close the reverse shell connection.

C.

Downgrade the svsaccount permissions.

D.

Remove the tester-created credentials.

Discussion
Nia
Why are these Dumps so important for students these days?
Mary Sep 27, 2026
With the constantly changing technology and advancements in the industry, it's important for students to have access to accurate and valid study material. Cramkey Dumps provide just that. They are constantly updated to reflect the latest changes and ensure that the information is up-to-date.
Lennie
I passed my exam and achieved wonderful score, I highly recommend it.
Emelia Sep 25, 2026
I think I'll give Cramkey a try next time I take a certification exam. Thanks for the recommendation!
Stefan
Thank you so much Cramkey I passed my exam today due to your highly up to date dumps.
Ocean Sep 8, 2026
Agree….Cramkey Dumps are constantly updated based on changes in the exams. They also have a team of experts who regularly review the materials to ensure their accuracy and relevance. This way, you can be sure you're studying the most up-to-date information available.
Everleigh
I must say that they are updated regularly to reflect the latest exam content, so you can be sure that you are getting the most accurate information. Plus, they are easy to use and understand, so even new students can benefit from them.
Huxley Sep 11, 2026
That's great to know. So, you think new students should buy these dumps?
Wyatt
Passed my exam… Thank you so much for your excellent Exam Dumps.
Arjun Sep 19, 2026
That sounds really useful. I'll definitely check it out.
Question 78

A security company has been contracted to perform a scoped insider-threat assessment to try to gain access to the human resources server that houses PII and salary data. The penetration testers have been given an internal network starting position.

Which of the following actions, if performed, would be ethical within the scope of the assessment?

Options:

A.

Exploiting a configuration weakness in the SQL database

B.

Intercepting outbound TLS traffic

C.

Gaining access to hosts by injecting malware into the enterprise-wide update server

D.

Leveraging a vulnerability on the internal CA to issue fraudulent client certificates

E.

Establishing and maintaining persistence on the domain controller

Discussion
Question 79

A penetration tester recently completed a review of the security of a core network device within a corporate environment. The key findings are as follows:

• The following request was intercepted going to the network device:

GET /login HTTP/1.1

Host: 10.50.100.16

User-Agent: Mozilla/5.0 (X11; Linux x86_64; rv:31.0) Gecko/20100101 Firefox/31.0

Accept-Language: en-US,en;q=0.5

Connection: keep-alive

Authorization: Basic WU9VUilOQU1FOnNlY3JldHBhc3N3b3jk

• Network management interfaces are available on the production network.

• An Nmap scan returned the following:
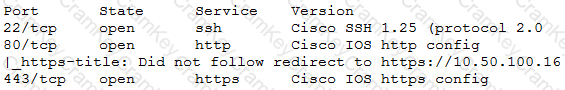
Questions 79

Which of the following would be BEST to add to the recommendations section of the final report? (Choose two.)

Options:

A.

Enforce enhanced password complexity requirements.

B.

Disable or upgrade SSH daemon.

C.

Disable HTTP/301 redirect configuration.

D.

Create an out-of-band network for management.

E.

Implement a better method for authentication.

F.

Eliminate network management and control interfaces.

Discussion
Page: 19 / 34
Title
Questions
Posted

PT0-002
PDF

$31.5  $104.99

PT0-002 Testing Engine

$37.5  $124.99

PT0-002 PDF + Testing Engine

$49.5  $164.99
