Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

CompTIA Updated PT0-002 Exam Questions and Answers by elowen

Page: 18 / 34

CompTIA PT0-002 Exam Overview :

Exam Name: CompTIA PenTest+ Certification Exam
Exam Code: PT0-002 Dumps
Vendor: CompTIA Certification: PenTest+
Questions: 464 Q&A's Shared By: elowen
Question 72

A penetration tester is testing a web application that is hosted by a public cloud provider. The tester is able to query the provider’s metadata and get the credentials used by the instance to authenticate itself. Which of the following vulnerabilities has the tester exploited?

Options:

A.

Cross-site request forgery

B.

Server-side request forgery

C.

Remote file inclusion

D.

Local file inclusion

Discussion
Question 73

Which of the following types of information would MOST likely be included in an application security assessment report addressed to developers? (Choose two.)

Options:

A.

Use of non-optimized sort functions

B.

Poor input sanitization

C.

Null pointer dereferences

D.

Non-compliance with code style guide

E.

Use of deprecated Javadoc tags

F.

A cydomatic complexity score of 3

Discussion
Question 74

A penetration tester conducted a discovery scan that generated the following:
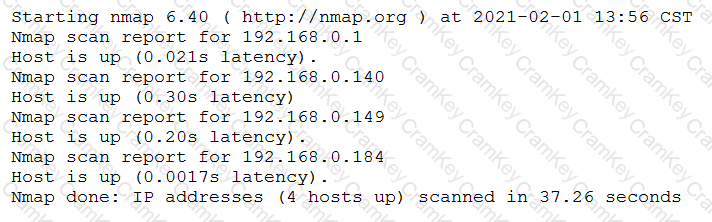
Questions 74

Which of the following commands generated the results above and will transform them into a list of active hosts for further analysis?

Options:

A.

nmap –oG list.txt 192.168.0.1-254 , sort

B.

nmap –sn 192.168.0.1-254 , grep “Nmap scan” | awk ‘{print S5}’

C.

nmap –-open 192.168.0.1-254, uniq

D.

nmap –o 192.168.0.1-254, cut –f 2

Discussion
Anaya
I found so many of the same questions on the real exam that I had already seen in the Cramkey Dumps. Thank you so much for making exam so easy for me. I passed it successfully!!!
Nina Oct 18, 2026
It's true! I felt so much more confident going into the exam because I had already seen and understood the questions.
Alaia
These Dumps are amazing! I used them to study for my recent exam and I passed with flying colors. The information in the dumps is so valid and up-to-date. Thanks a lot!!!
Zofia Oct 21, 2026
That's great to hear! I've been struggling to find good study material for my exam. I will ty it for sure.
Carson
Yeah, definitely. I would definitely recommend Cramkey Dumps to anyone who is preparing for an exam.
Rufus Oct 9, 2026
Me too. They're a lifesaver!
Ivan
I tried these dumps for my recent certification exam and I found it pretty helpful.
Elis Oct 16, 2026
Agree!!! The questions in the dumps were quite similar to what came up in the actual exam. It gave me a good idea of the types of questions to expect and helped me revise efficiently.
Melody
My experience with Cramkey was great! I was surprised to see that many of the questions in my exam appeared in the Cramkey dumps.
Colby Oct 22, 2026
Yes, In fact, I got a score of above 85%. And I attribute a lot of my success to Cramkey's dumps.
Question 75

Which of the following should a penetration tester attack to gain control of the state in the HTTP protocol after the user is logged in?

Options:

A.

HTTPS communication

B.

Public and private keys

C.

Password encryption

D.

Sessions and cookies

Discussion
Page: 18 / 34
Title
Questions
Posted

PT0-002
PDF

$27.5  $109.99

PT0-002 Testing Engine

$32.5  $129.99

PT0-002 PDF + Testing Engine

$42.5  $169.99
