Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

CompTIA Updated PT0-002 Exam Questions and Answers by trent

Page: 2 / 34

CompTIA PT0-002 Exam Overview :

Exam Name: CompTIA PenTest+ Certification Exam
Exam Code: PT0-002 Dumps
Vendor: CompTIA Certification: PenTest+
Questions: 464 Q&A's Shared By: trent
Question 8

During an assessment, a penetration tester was able to access the organization's wireless network from outside of the building using a laptop running Aircrack-ng. Which of the following should be recommended to the client to remediate this issue?

Options:

A.

Changing to Wi-Fi equipment that supports strong encryption

B.

Using directional antennae

C.

Using WEP encryption

D.

Disabling Wi-Fi

Discussion
Question 9

A penetration tester gives the following command to a systems administrator to execute on one of the target servers:

rm -f /var/www/html/G679h32gYu.php

Which of the following BEST explains why the penetration tester wants this command executed?

Options:

A.

To trick the systems administrator into installing a rootkit

B.

To close down a reverse shell

C.

To remove a web shell after the penetration test

D.

To delete credentials the tester created

Discussion
Question 10

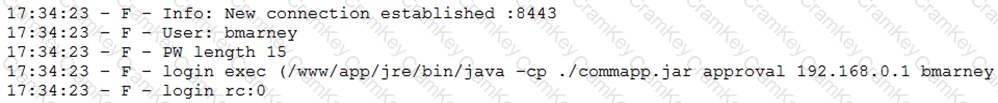
A penetration tester downloaded a Java application file from a compromised web server and identifies how to invoke it by looking at the following log:
Questions 10

Which of the following is the order of steps the penetration tester needs to follow to validate whether the Java application uses encryption over sockets?

Options:

A.

Run an application vulnerability scan and then identify the TCP ports used by the application.

B.

Run the application attached to a debugger and then review the application's log.

C.

Disassemble the binary code and then identify the break points.

D.

Start a packet capture with Wireshark and then run the application.

Discussion
Question 11

A security firm has been hired to perform an external penetration test against a company. The only information the firm received was the company name. Which of the following passive reconnaissance approaches would be MOST likely to yield positive initial results?

Options:

A.

Specially craft and deploy phishing emails to key company leaders.

B.

Run a vulnerability scan against the company's external website.

C.

Runtime the company's vendor/supply chain.

D.

Scrape web presences and social-networking sites.

Discussion
Kylo
What makes Cramkey Dumps so reliable? Please guide.
Sami Oct 20, 2026
Well, for starters, they have a team of experts who are constantly updating their material to reflect the latest changes in the industry. Plus, they have a huge database of questions and answers, which makes it easy to study and prepare for the exam.
Miriam
Highly recommended Dumps. 100% authentic and reliable. Passed my exam with wonderful score.
Milan Oct 22, 2026
I see. Thanks for the information. I'll definitely keep Cramkey in mind for my next exam.
Lennie
I passed my exam and achieved wonderful score, I highly recommend it.
Emelia Oct 23, 2026
I think I'll give Cramkey a try next time I take a certification exam. Thanks for the recommendation!
Ilyas
Definitely. I felt much more confident and prepared because of the Cramkey Dumps. I was able to answer most of the questions with ease and I think that helped me to score well on the exam.
Saoirse Oct 26, 2026
That's amazing. I'm glad you found something that worked for you. Maybe I should try them out for my next exam.
Page: 2 / 34
Title
Questions
Posted

PT0-002
PDF

$27.5  $109.99

PT0-002 Testing Engine

$32.5  $129.99

PT0-002 PDF + Testing Engine

$42.5  $169.99
