Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

ECCouncil Updated EC0-350 Exam Questions and Answers by yasmin

Page: 29 / 32

ECCouncil EC0-350 Exam Overview :

Exam Name: Ethical Hacking and Countermeasures V8
Exam Code: EC0-350 Dumps
Vendor: ECCouncil Certification: Certified Ethical Hacker
Questions: 878 Q&A's Shared By: yasmin
Question 116

Bob reads an article about how insecure wireless networks can be. He gets approval from his management to implement a policy of not allowing any wireless devices on the network. What other steps does Bob have to take in order to successfully implement this? (Select 2 answer.)

Options:

A.

Train users in the new policy.

B.

Disable all wireless protocols at the firewall.

C.

Disable SNMP on the network so that wireless devices cannot be configured.

D.

Continuously survey the area for wireless devices.

Discussion
Erik
Hey, I have passed my exam using Cramkey Dumps?
Freyja Oct 5, 2026
Really, what are they? All come in your pool? Please give me more details, I am going to have access their subscription. Please brother, give me more details.
Mylo
Excellent dumps with authentic information… I passed my exam with brilliant score.
Dominik Oct 12, 2026
That's amazing! I've been looking for good study material that will help me prepare for my upcoming certification exam. Now, I will try it.
Melody
My experience with Cramkey was great! I was surprised to see that many of the questions in my exam appeared in the Cramkey dumps.
Colby Oct 22, 2026
Yes, In fact, I got a score of above 85%. And I attribute a lot of my success to Cramkey's dumps.
Alessia
Amazing Dumps. Found almost all questions in actual exam whih I prepared from these valuable dumps. Recommended!!!!
Belle Oct 28, 2026
That's impressive. I've been struggling with finding good study material for my certification. Maybe I should give Cramkey Dumps a try.
Vienna
I highly recommend them. They are offering exact questions that we need to prepare our exam.
Jensen Oct 3, 2026
That's great. I think I'll give Cramkey a try next time I take a certification exam. Thanks for the recommendation!
Question 117

In order to attack a wireless network, you put up an access point and override the signal of the real access point. As users send authentication data, you are able to capture it. What kind of attack is this?

Options:

A.

WEP attack

B.

Drive by hacking

C.

Rogue access point attack

D.

Unauthorized access point attack

Discussion
Question 118

Sally is a network admin for a small company. She was asked to install wireless accesspoints in the building. In looking at the specifications for the access-points, she sees that all of them offer WEP. Which of these are true about WEP?

Select the best answer.

Options:

A.

Stands for Wireless Encryption Protocol

B.

It makes a WLAN as secure as a LAN

C.

Stands for Wired Equivalent Privacy

D.

It offers end to end security

Discussion
Question 119

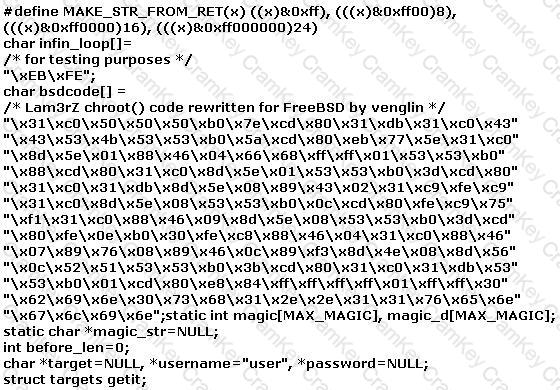
The following exploit code is extracted from what kind of attack?

Questions 119

Options:

A.

Remote password cracking attack

B.

SQL Injection

C.

Distributed Denial of Service

D.

Cross Site Scripting

E.

Buffer Overflow

Discussion
Page: 29 / 32
Title
Questions
Posted

EC0-350
PDF

$38.5  $109.99

EC0-350 Testing Engine

$45.5  $129.99

EC0-350 PDF + Testing Engine

$59.5  $169.99