Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

ECCouncil Updated EC0-350 Exam Questions and Answers by alastair

Page: 32 / 32

ECCouncil EC0-350 Exam Overview :

Exam Name: Ethical Hacking and Countermeasures V8
Exam Code: EC0-350 Dumps
Vendor: ECCouncil Certification: Certified Ethical Hacker
Questions: 878 Q&A's Shared By: alastair
Question 128

In which location, SAM hash passwords are stored in Windows 7?

Options:

A.

c:\windows\system32\config\SAM

B.

c:\winnt\system32\machine\SAM

C.

c:\windows\etc\drivers\SAM

D.

c:\windows\config\etc\SAM

Discussion
Melody
My experience with Cramkey was great! I was surprised to see that many of the questions in my exam appeared in the Cramkey dumps.
Colby Oct 22, 2026
Yes, In fact, I got a score of above 85%. And I attribute a lot of my success to Cramkey's dumps.
Marley
Hey, I heard the good news. I passed the certification exam!
Jaxson Oct 1, 2026
Yes, I passed too! And I have to say, I couldn't have done it without Cramkey Dumps.
Stefan
Thank you so much Cramkey I passed my exam today due to your highly up to date dumps.
Ocean Oct 12, 2026
Agree….Cramkey Dumps are constantly updated based on changes in the exams. They also have a team of experts who regularly review the materials to ensure their accuracy and relevance. This way, you can be sure you're studying the most up-to-date information available.
Nell
Are these dumps reliable?
Ernie Oct 21, 2026
Yes, very much so. Cramkey Dumps are created by experienced and certified professionals who have gone through the exams themselves. They understand the importance of providing accurate and relevant information to help you succeed.
Ari
Can anyone explain what are these exam dumps and how are they?
Ocean Oct 9, 2026
They're exam preparation materials that are designed to help you prepare for various certification exams. They provide you with up-to-date and accurate information to help you pass your exams.
Question 129

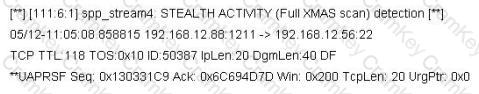
Jason is the network administrator of Spears Technology. He has enabled SNORT IDS to detect attacks going through his network. He receives Snort SMS alerts on his iPhone whenever there is an attempted intrusion to his network.

He receives the following SMS message during the weekend.
Questions 129

An attacker Chew Siew sitting in Beijing, China had just launched a remote scan on Jason's network with the hping command.

Which of the following hping2 command is responsible for the above snort alert?

Options:

A.

chenrocks:/home/siew # hping -S -R -P -A -F -U 192.168.2.56 -p 22 -c 5 -t 118

B.

chenrocks:/home/siew # hping -F -Q -J -A -C -W 192.168.2.56 -p 22 -c 5 -t 118

C.

chenrocks:/home/siew # hping -D -V -R -S -Z -Y 192.168.2.56 -p 22 -c 5 -t 118

D.

chenrocks:/home/siew # hping -G -T -H -S -L -W 192.168.2.56 -p 22 -c 5 -t 118

Discussion
Question 130

File extensions provide information regarding the underlying server technology. Attackers can use this information to search vulnerabilities and launch attacks. How would you disable file extensions in Apache servers?

Options:

A.

Use disable-eXchange

B.

Use mod_negotiation

C.

Use Stop_Files

D.

Use Lib_exchanges

Discussion
Question 131

While testing web applications, you attempt to insert the following test script into the search area on the company's web site:

Later, when you press the search button, a pop up box appears on your screen with the text "Testing Testing Testing". What vulnerability is detected in the web application here?

Options:

A.

Cross Site Scripting

B.

Password attacks

C.

A Buffer Overflow

D.

A hybrid attack

Discussion
Page: 32 / 32
Title
Questions
Posted

EC0-350
PDF

$27.5  $109.99

EC0-350 Testing Engine

$32.5  $129.99

EC0-350 PDF + Testing Engine

$42.5  $169.99
