Pre-Winter Sale Limited Time 65% Discount Offer - Ends in 0d 00h 00m 00s - Coupon code: get65

GAQM Updated CEH-001 Exam Questions and Answers by carson

Page: 13 / 32

GAQM CEH-001 Exam Overview :

Exam Name: Certified Ethical Hacker (CEH)
Exam Code: CEH-001 Dumps
Vendor: GAQM Certification: Certified Ethical Hacker CEH
Questions: 878 Q&A's Shared By: carson
Question 52

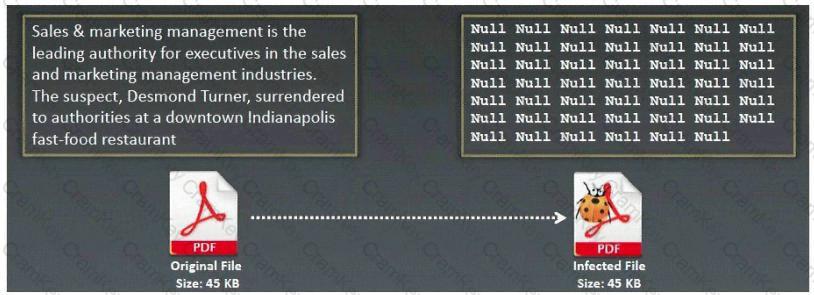
What type of Virus is shown here?

Questions 52

Options:

A.

Macro Virus

B.

Cavity Virus

C.

Boot Sector Virus

D.

Metamorphic Virus

E.

Sparse Infector Virus

Discussion
Question 53

Nathan is testing some of his network devices. Nathan is using Macof to try and flood the ARP cache of these switches. If these switches' ARP cache is successfully flooded, what will be the result?

Options:

A.

The switches will drop into hub mode if the ARP cache is successfully flooded.

B.

If the ARP cache is flooded, the switches will drop into pix mode making it less susceptible to attacks.

C.

Depending on the switch manufacturer, the device will either delete every entry in its ARP cache or reroute packets to the nearest switch.

D.

The switches will route all traffic to the broadcast address created collisions.

Discussion
Inaya
Passed the exam. questions are valid. The customer support is top-notch. They were quick to respond to any questions I had and provided me with all the information I needed.
Cillian Sep 22, 2026
That's a big plus. I've used other dump providers in the past and the customer support was often lacking.
Freddy
I passed my exam with flying colors and I'm confident who will try it surely ace the exam.
Aleksander Sep 1, 2026
Thanks for the recommendation! I'll check it out.
Lennie
I passed my exam and achieved wonderful score, I highly recommend it.
Emelia Sep 25, 2026
I think I'll give Cramkey a try next time I take a certification exam. Thanks for the recommendation!
Joey
I highly recommend Cramkey Dumps to anyone preparing for the certification exam. They have all the key information you need and the questions are very similar to what you'll see on the actual exam.
Dexter Sep 18, 2026
Agreed. It's definitely worth checking out if you're looking for a comprehensive and reliable study resource.
Anya
I must say they're considered the best dumps available and the questions are very similar to what you'll see in the actual exam. Recommended!!!
Cassius Sep 6, 2026
Yes, they offer a 100% success guarantee. And many students who have used them have reported passing their exams with flying colors.
Question 54

Bob was frustrated with his competitor, Brownies Inc., and decided to launch an attack that would result in serious financial losses. He planned the attack carefully and carried out the attack at the appropriate moment.

Meanwhile, Trent, an administrator at Brownies Inc., realized that their main financial transaction server had been attacked. As a result of the attack, the server crashed and Trent needed to reboot the system, as no one was able to access the resources of the company. This process involves human interaction to fix it.

What kind of Denial of Service attack was best illustrated in the scenario above?

Options:

A.

Simple DDoS attack

B.

DoS attacks which involves flooding a network or system

C.

DoS attacks which involves crashing a network or system

D.

DoS attacks which is done accidentally or deliberately

Discussion
Question 55

When a normal TCP connection starts, a destination host receives a SYN (synchronize/start) packet from a source host and sends back a SYN/ACK (synchronize acknowledge). The destination host must then hear an ACK (acknowledge) of the SYN/ACK before the connection is established. This is referred to as the "TCP three-way handshake." While waiting for the ACK to the SYN ACK, a connection queue of finite size on the destination host keeps track of connections waiting to be completed. This queue typically empties quickly since the ACK is expected to arrive a few milliseconds after the SYN ACK. How would an attacker exploit this design by launching TCP SYN attack?
Options:

A.

Attacker generates TCP SYN packets with random destination addresses towards a victim host

B.

Attacker floods TCP SYN packets with random source addresses towards a victim host

C.

Attacker generates TCP ACK packets with random source addresses towards a victim host

D.

Attacker generates TCP RST packets with random source addresses towards a victim host

Discussion
Page: 13 / 32
Title
Questions
Posted

CEH-001
PDF

$36.75  $104.99

CEH-001 Testing Engine

$43.75  $124.99

CEH-001 PDF + Testing Engine

$57.75  $164.99