Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

Splunk Updated SPLK-1005 Exam Questions and Answers by arla

Page: 2 / 5

Splunk SPLK-1005 Exam Overview :

Exam Name: Splunk Cloud Certified Admin
Exam Code: SPLK-1005 Dumps
Vendor: Splunk Certification: Splunk Cloud Certified Admin
Questions: 82 Q&A's Shared By: arla
Question 8

In Splunk terminology, what is an index?

Options:

A.

A data repository that contains raw, compressed data along with psidx files.

B.

A data repository that contains raw, compressed data along with tsidx files.

C.

A data repository that contains raw, uncompressed data along with psidx files.

D.

A data repository that contains raw, uncompressed data along with tsidx files.

Discussion
Ilyas
Definitely. I felt much more confident and prepared because of the Cramkey Dumps. I was able to answer most of the questions with ease and I think that helped me to score well on the exam.
Saoirse Oct 26, 2026
That's amazing. I'm glad you found something that worked for you. Maybe I should try them out for my next exam.
Wyatt
Passed my exam… Thank you so much for your excellent Exam Dumps.
Arjun Oct 19, 2026
That sounds really useful. I'll definitely check it out.
Melody
My experience with Cramkey was great! I was surprised to see that many of the questions in my exam appeared in the Cramkey dumps.
Colby Oct 22, 2026
Yes, In fact, I got a score of above 85%. And I attribute a lot of my success to Cramkey's dumps.
Inaya
Passed the exam. questions are valid. The customer support is top-notch. They were quick to respond to any questions I had and provided me with all the information I needed.
Cillian Oct 21, 2026
That's a big plus. I've used other dump providers in the past and the customer support was often lacking.
Ayra
How these dumps are necessary for passing the certification exam?
Damian Oct 20, 2026
They give you a competitive edge and help you prepare better.
Question 9

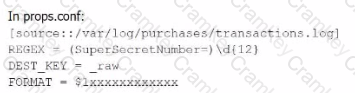
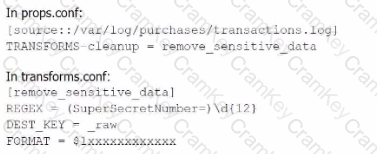
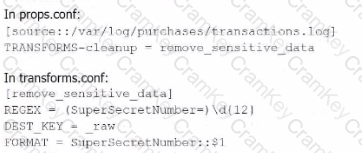
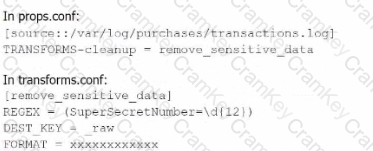
A user has been asked to mask some sensitive data without tampering with the structure of the file /var/log/purchase/transactions. log that has the following format:
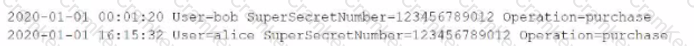
Questions 9

A)

Questions 9

B)

Questions 9

C)

Questions 9

D)

Questions 9

Options:

A.

Option A

B.

Option B

C.

Option C

D.

Option D

Discussion
Question 10

A monitor has been created in inputs. con: for a directory that contains a mix of file types.

How would a Cloud Admin fine-tune assigned sourcetypes for different files in the directory during the input phase?

Options:

A.

On the Indexer parsing the data, leave sourcetype as automatic for the directory monitor. Then create a props.conf that assigns a specific sourcetype by source stanza.

B.

On the forwarder collecting the data, leave sourcetype as automatic for the directory monitor. Then create a props. conf that assigns a specific sourcetype by source stanza.

C.

On the Indexer parsing the data, set multiple sourcetype_source attributes for the directory monitor collecting the files. Then create a props, com that filters out unwanted files.

D.

On the forwarder collecting the data, set multiple 3ourcotype_sourc« attributes for the directory monitor collecting the files. Then create a props. conf that filters out unwanted files.

Discussion
Question 11

Which of the following is not a path used by Splunk to execute scripts?

Options:

A.

SPLUNK_HOME/etc/system/bin

B.

SPLUNK HOME/etc/appa//bin

C.

SPLUNKHOMS/ctc/scripts/local

D.

SPLUNK_HOME/bin/scripts

Discussion
Page: 2 / 5

SPLK-1005
PDF

$27.5  $109.99

SPLK-1005 Testing Engine

$32.5  $129.99

SPLK-1005 PDF + Testing Engine

$42.5  $169.99