Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

ECCouncil Updated 312-96 Exam Questions and Answers by nour

Page: 2 / 3

ECCouncil 312-96 Exam Overview :

Exam Name: Certified Application Security Engineer (CASE) JAVA
Exam Code: 312-96 Dumps
Vendor: ECCouncil Certification: Application Security
Questions: 47 Q&A's Shared By: nour
Question 8

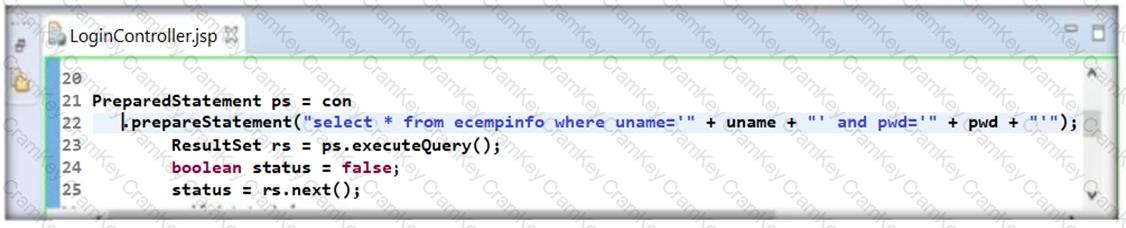
During his secure code review, John, an independent application security expert, found that the developer has used Java code as highlighted in the following screenshot. Identify the security mistake committed by the developer?
Questions 8

Options:

A.

He is trying to use Whitelisting Input Validation

B.

He is trying to use Non-parametrized SQL query

C.

He is trying to use Blacklisting Input Validation

D.

He is trying to use Parametrized SQL Query

Discussion
Question 9

Which of the following method will you use in place of ex.printStackTrace() method to avoid printing stack trace on error?

Options:

A.

ex.StackTrace.getError();

B.

ex.message();

C.

ex.getMessage();

D.

ex.getError();

Discussion
Question 10

The threat modeling phase where applications are decomposed and their entry points are reviewed from an attacker's perspective is known as ________

Options:

A.

Attack Surface Evaluation

B.

Threat Classification

C.

Threat Identification

D.

Impact Analysis

Discussion
Fatima
Hey I passed my exam. The world needs to know about it. I have never seen real exam questions on any other exam preparation resource like I saw on Cramkey Dumps.
Niamh Oct 1, 2026
That's true. Cramkey Dumps are simply the best when it comes to preparing for the certification exam. They have all the key information you need and the questions are very similar to what you'll see on the actual exam.
River
Hey, I used Cramkey Dumps to prepare for my recent exam and I passed it.
Lewis Oct 26, 2026
Yeah, I used these dumps too. And I have to say, I was really impressed with the results.
Kylo
What makes Cramkey Dumps so reliable? Please guide.
Sami Oct 20, 2026
Well, for starters, they have a team of experts who are constantly updating their material to reflect the latest changes in the industry. Plus, they have a huge database of questions and answers, which makes it easy to study and prepare for the exam.
Syeda
I passed, Thank you Cramkey for your precious Dumps.
Stella Oct 7, 2026
That's great. I think I'll give Cramkey Dumps a try.
Anaya
I found so many of the same questions on the real exam that I had already seen in the Cramkey Dumps. Thank you so much for making exam so easy for me. I passed it successfully!!!
Nina Oct 18, 2026
It's true! I felt so much more confident going into the exam because I had already seen and understood the questions.
Question 11

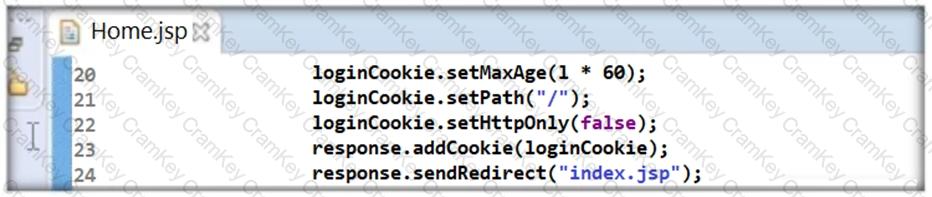
Thomas is not skilled in secure coding. He neither underwent secure coding training nor is aware of the consequences of insecure coding. One day, he wrote code as shown in the following screenshot. He passed 'false' parameter to setHttpOnly() method that may result in the existence of a certain type of vulnerability. Identify the attack that could exploit the vulnerability in the above case.

Questions 11

Options:

A.

Denial-of-Service attack

B.

Client-Side Scripts Attack

C.

SQL Injection Attack

D.

Directory Traversal Attack

Discussion
Page: 2 / 3

312-96
PDF

$27.5  $109.99

312-96 Testing Engine

$32.5  $129.99

312-96 PDF + Testing Engine

$42.5  $169.99
