Black Friday VIP Weekend - 75% Discount offer - Ends in 0d 00h 00m 00s - Coupon code: 75brite

ECCouncil Updated 412-79v10 Exam Questions and Answers by zayd

Page: 5 / 7

ECCouncil 412-79v10 Exam Overview :

Exam Name: EC-Council Certified Security Analyst (ECSA) V10
Exam Code: 412-79v10 Dumps
Vendor: ECCouncil Certification: ECSA
Questions: 201 Q&A's Shared By: zayd
Question 20

What is the following command trying to accomplish?

Questions 20

Options:

A.

Verify that NETBIOS is running for the 192.168.0.0 network

B.

Verify that TCP port 445 is open for the 192.168.0.0 network

C.

Verify that UDP port 445 is open for the 192.168.0.0 network

D.

Verify that UDP port 445 is closed for the 192.168.0.0 networks

Discussion
Question 21

You work as an IT security auditor hired by a law firm in Boston to test whether you can gain access to sensitive information about the company clients. You have rummaged through their trash and found very little information.

You do not want to set off any alarms on their network, so you plan on performing passive foot printing against their Web servers. What tool should you use?

Options:

A.

Nmap

B.

Netcraft

C.

Ping sweep

D.

Dig

Discussion
Question 22

An attacker injects malicious query strings in user input fields to bypass web service authentication mechanisms and to access back-end databases. Which of the following attacks is this?

Options:

A.

Frame Injection Attack

B.

LDAP Injection Attack

C.

XPath Injection Attack

D.

SOAP Injection Attack

Discussion
Question 23

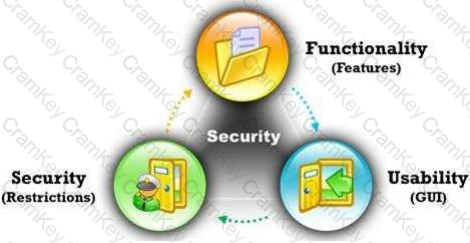
Today, most organizations would agree that their most valuable IT assets reside within applications and databases. Most would probably also agree that these are areas that have the weakest levels of security, thus making them the prime target for malicious activity from system administrators, DBAs, contractors, consultants, partners, and customers.
Questions 23

Which of the following flaws refers to an application using poorly written encryption code to securely encrypt and store sensitive data in the database and allows an attacker to steal or modify weakly protected data such as credit card numbers, SSNs, and other authentication credentials?

Options:

A.

SSI injection attack

B.

Insecure cryptographic storage attack

C.

Hidden field manipulation attack

D.

Man-in-the-Middle attack

Discussion
Reeva
Wow what a success I achieved today. Thank you so much Cramkey for amazing Dumps. All students must try it.
Amari Oct 27, 2026
Wow, that's impressive. I'll definitely keep Cramkey in mind for my next exam.
Andrew
Are these dumps helpful?
Jeremiah Oct 12, 2026
Yes, Don’t worry!!! I'm confident you'll find them to be just as helpful as I did. Good luck with your exam!
Kylo
What makes Cramkey Dumps so reliable? Please guide.
Sami Oct 20, 2026
Well, for starters, they have a team of experts who are constantly updating their material to reflect the latest changes in the industry. Plus, they have a huge database of questions and answers, which makes it easy to study and prepare for the exam.
Aryan
Absolutely rocked! They are an excellent investment for anyone who wants to pass the exam on the first try. They save you time and effort by providing a comprehensive overview of the exam content, and they give you a competitive edge by giving you access to the latest information. So, I definitely recommend them to new students.
Jessie Oct 23, 2026
did you use PDF or Engine? Which one is most useful?
Ernest
That's amazing. I think I'm going to give Cramkey Dumps a try for my next exam. Thanks for telling me about them! CramKey admin please share more questions……You guys are amazing.
Nate Oct 12, 2026
I failed last week, I never know this site , but amazed to see all these questions were in my exam week before. I feel bad now, why I didn’t bother this site. Thanks Cramkey, Excellent Job.
Page: 5 / 7

412-79v10
PDF

$27.5  $109.99

412-79v10 Testing Engine

$32.5  $129.99

412-79v10 PDF + Testing Engine

$42.5  $169.99
